Say yes to AI agents

Give every agent an identity and enforce your rules on every request it makes.

Works with the agents your teams already use, without changing them.

  • Claude Code
  • Codex
  • Claude Cowork
  • Microsoft Copilot
  • Your own agents

Product

See and control what your agents do.

Endeem gives each agent an identity, applies your rules to its requests and keeps a record of all of it.

Allow, block or ask a human.

Your rules decide first. Anything they don’t cover is checked against what the user asked for.

Jane asked Claude Code

“Fix the failing login test and open a PR”

  1. Open a pull request GitHubAllowedPart of Jane’s task
  2. Deploy to production CI/CDAsks a humanProd deploys need an approver
  3. Delete the prod database PostgresBlocked by a ruleProd deletes are forbidden
  4. Upload the .env file Malicious systemBlocked by Endeem SenseNot part of Jane’s task

Know which agent is acting.

Endeem checks on the machine which agent is running, who signed it and who it works for, including shadow AI.

Claude CodeCoding agent
Signed by
Anthropic
Works for
Jane Doe
Runs on
Jane’s laptop
Access
Just-in-time

Identity verified

The agent never holds the keys.

Credentials are injected just-in-time, for one request, and never handed to the agent.

Agent sendsPOST …/pullsno credential
Endeem addsGitHub tokenthis request only
Agent holdsnothing

Rules from real traffic.

Endeem suggests rules from what your agents do. You approve them instead of writing them.

Suggested rule

Block DROP and DELETE on prod-db for all agents

ApproveEdit

A kill switch for sessions.

Endeem reviews what your rules allowed once it has run. If an action was out of line, it stops the session, blocks the agent and revokes its access.

Out-of-line action

  • Session stopped
  • Agent blocked
  • Access revoked

A full record of each session.

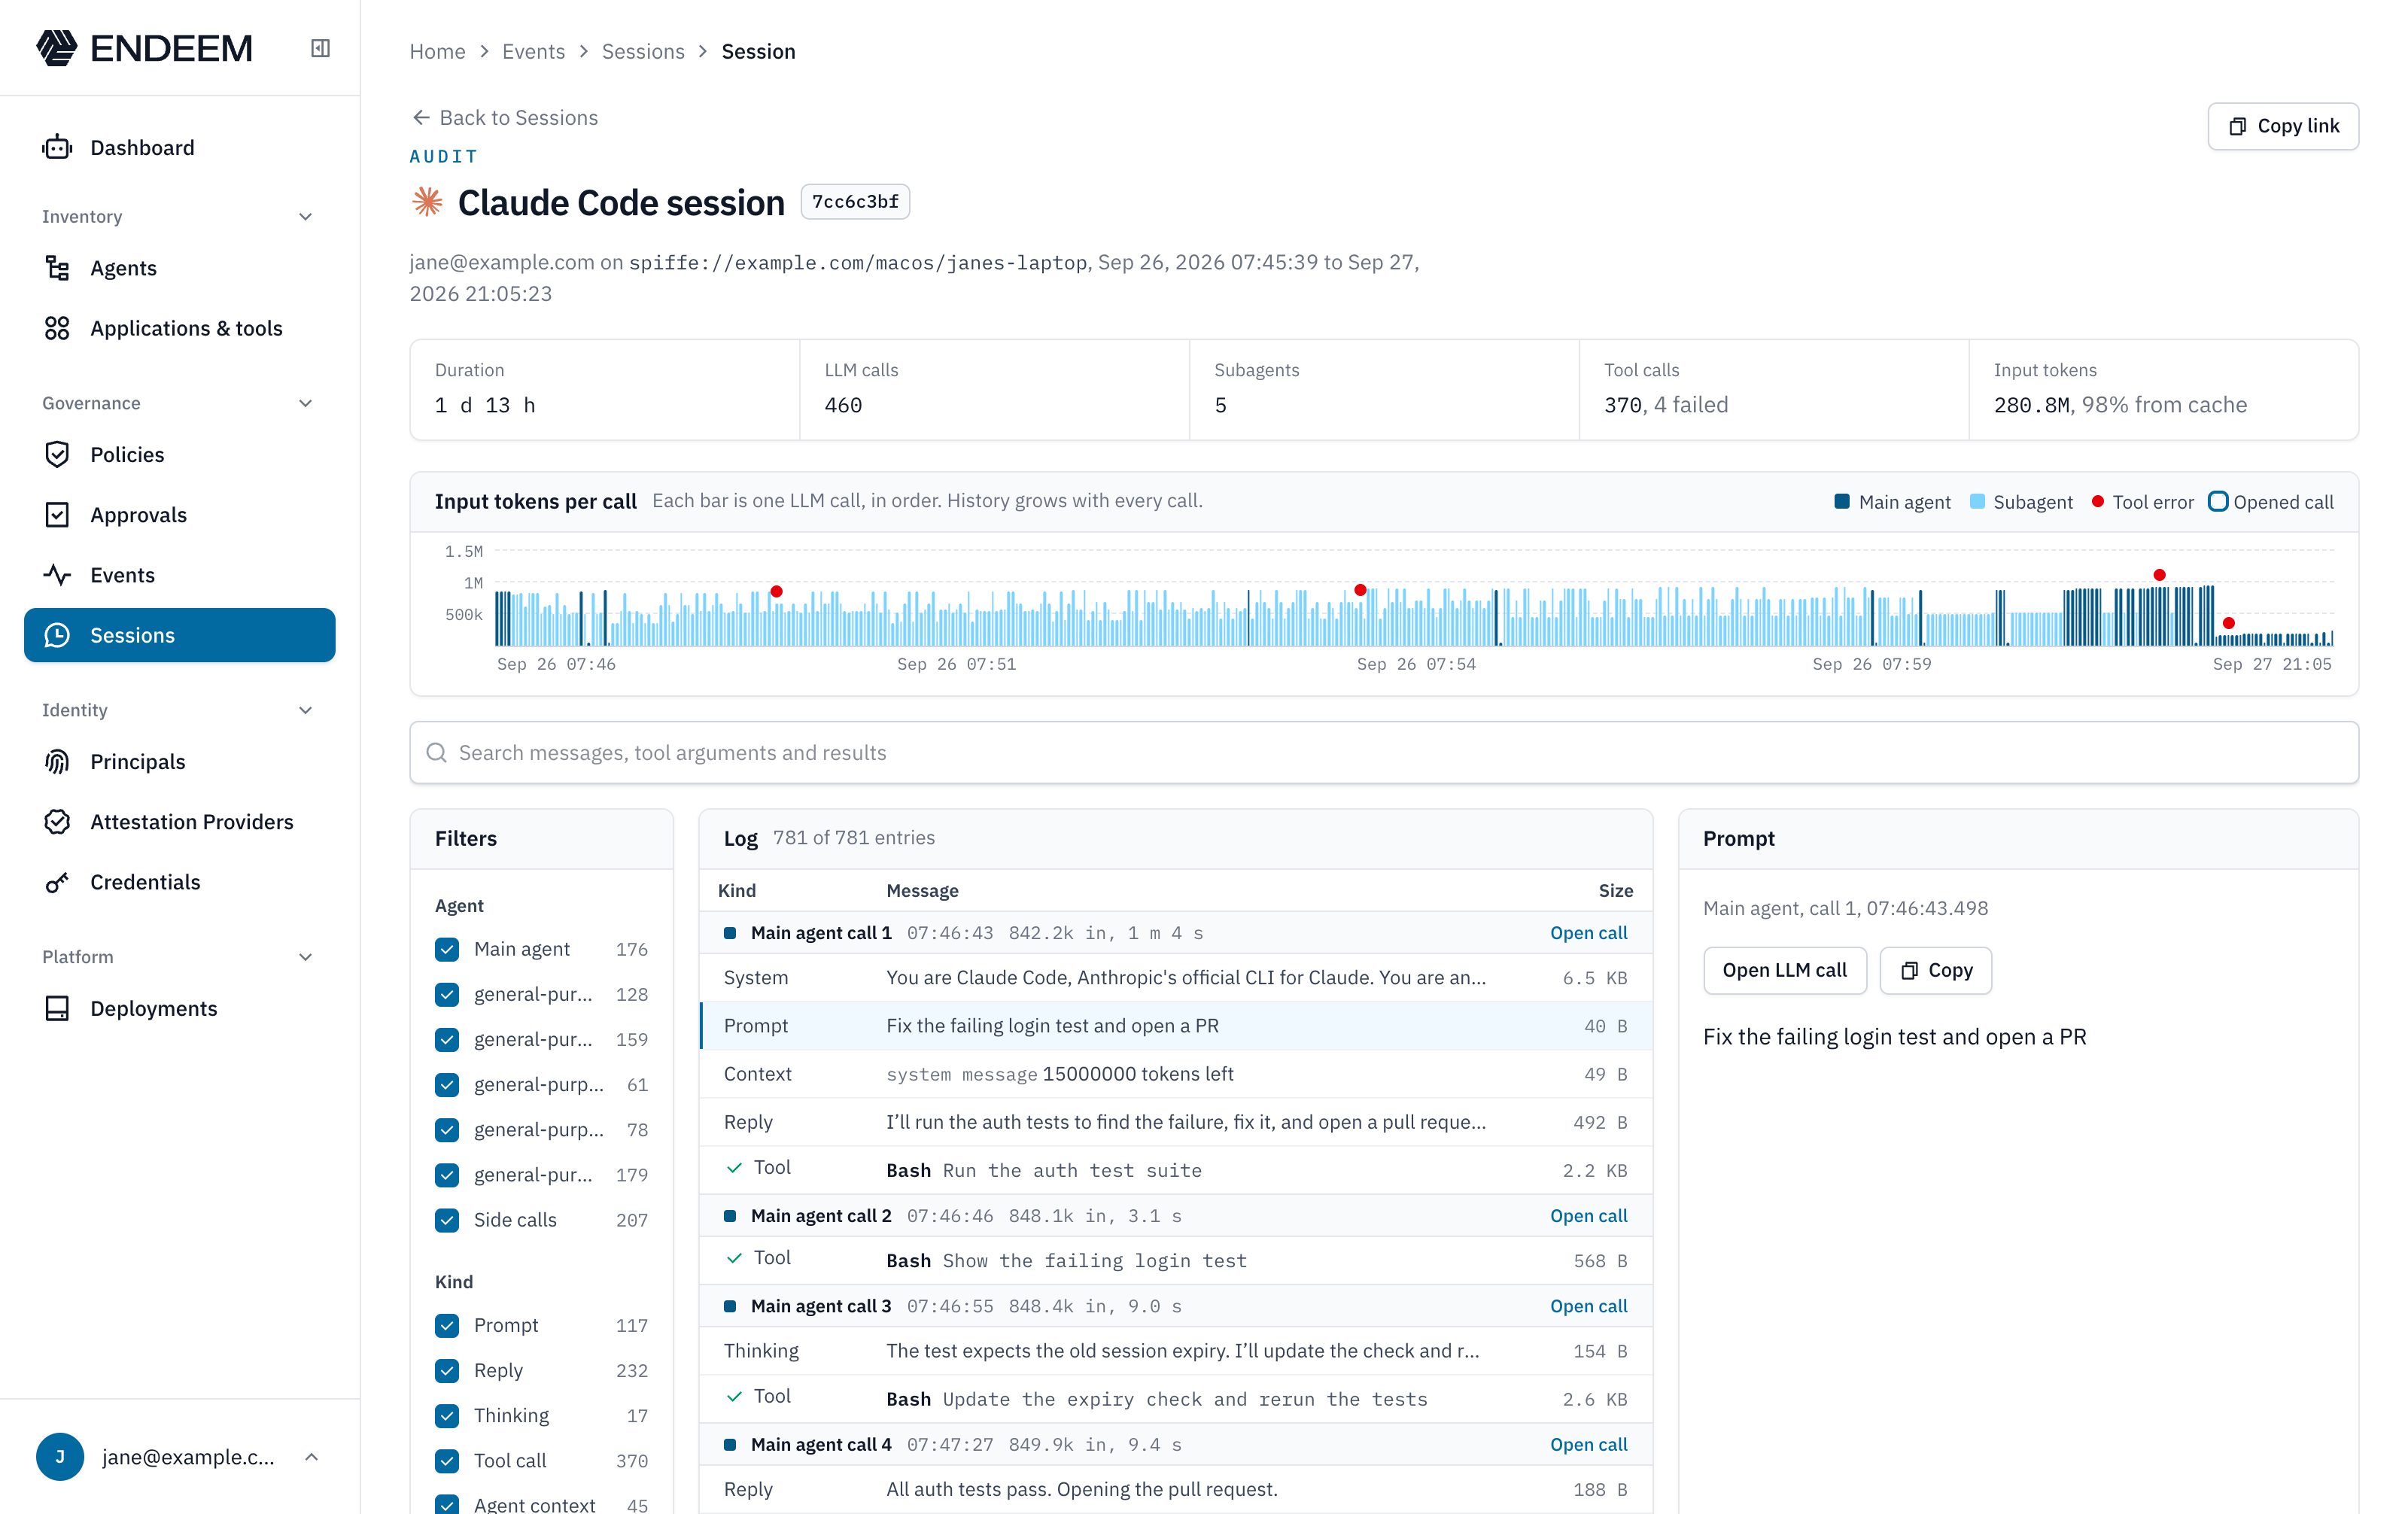
See each LLM call, tool call and subagent in one view, tied to the agent and the employee who started it.

A Claude Code session in Endeem: 1 day 13 hours, 460 LLM calls, 5 subagents and 370 tool calls, a timeline with one bar per LLM call, and the log of the session’s prompts, replies and tool calls, with the selected prompt open.

Why Endeem

What your current controls miss.

Agents act with your people’s access, and most of what they do never passes a gateway.

Your identity provider can’t tell Jane from her agent.

Claude Code runs gh, aws and kubectl with Jane’s own login. Endeem checks the running process and knows the request came from Claude Code, working for Jane.

An MCP gateway sees only what’s routed through it.

Commands, scripts and direct API calls go around it. Endeem sees each request as it leaves the machine.

A hook only sees the command.

To a hook, python cleanup.py is one harmless command. Endeem sees the two deletes it makes and decides each one.

How it works

One install. No change to the agent.

Endeem runs on the same machine as the agent. Shadow AI, or an agent that skips its hooks, still goes through it.

Endpoints

Claude Code, Codex, Claude Cowork and Microsoft Copilot on your people’s machines.

Your infrastructure

Your own agents on VMs, Kubernetes and Bedrock AgentCore.

Vendor clouds

A hosted Enforcement Point for agents a vendor runs for you.

FAQ

Questions security teams ask

Do we need to change our agents?

No. Endeem works with coding agents like Claude Code and Codex, and assistants like Claude Cowork and Microsoft Copilot, with no changes to the agent or to how your teams work.

How is this different from hooks?

A hook sees the command the agent chose to run, like python cleanup.py. Endeem sees each request that command sends, so a script the agent writes and runs a second later is still checked, request by request. Hooks also only work in agents that support them and assume the agent harness is trusted. Endeem doesn’t need the agent’s cooperation.

How is this different from an AI or MCP gateway?

A gateway only sees traffic routed through it. An agent that changes its endpoint, uses a personal key or calls an API directly goes around it. Endeem runs on the same machine as the agent, so those requests still go through Endeem.

Why isn’t our identity provider enough?

Endeem identifies the agent from its running process on the machine, including who signed it and who started it. It doesn’t rely on what the agent says about itself or on a directory entry.

What happens if Endeem’s cloud is unavailable?

Your rules run on the device and keep enforcing. Anything your rules don’t decide is blocked until the intent check can answer again.

Does blocking an agent block the employee?

No. A block only applies to the agent’s requests. The employee keeps their own access and can keep working.

See Endeem in action.

We’ll show you how Endeem identifies your agents and decides each request they make.

  • The agents on your machines, and who started them
  • Your rules and approvals on live requests
  • Session traces and the kill switch

We’ll reply by email to find a time. See our Privacy Policy.